

A standard file for publishing security testing rules
hacker.txt is a spec and a generator. A website publishes one text file saying what security testing is allowed, where, and under which limits. Ethical hackers and automated tools can read it.
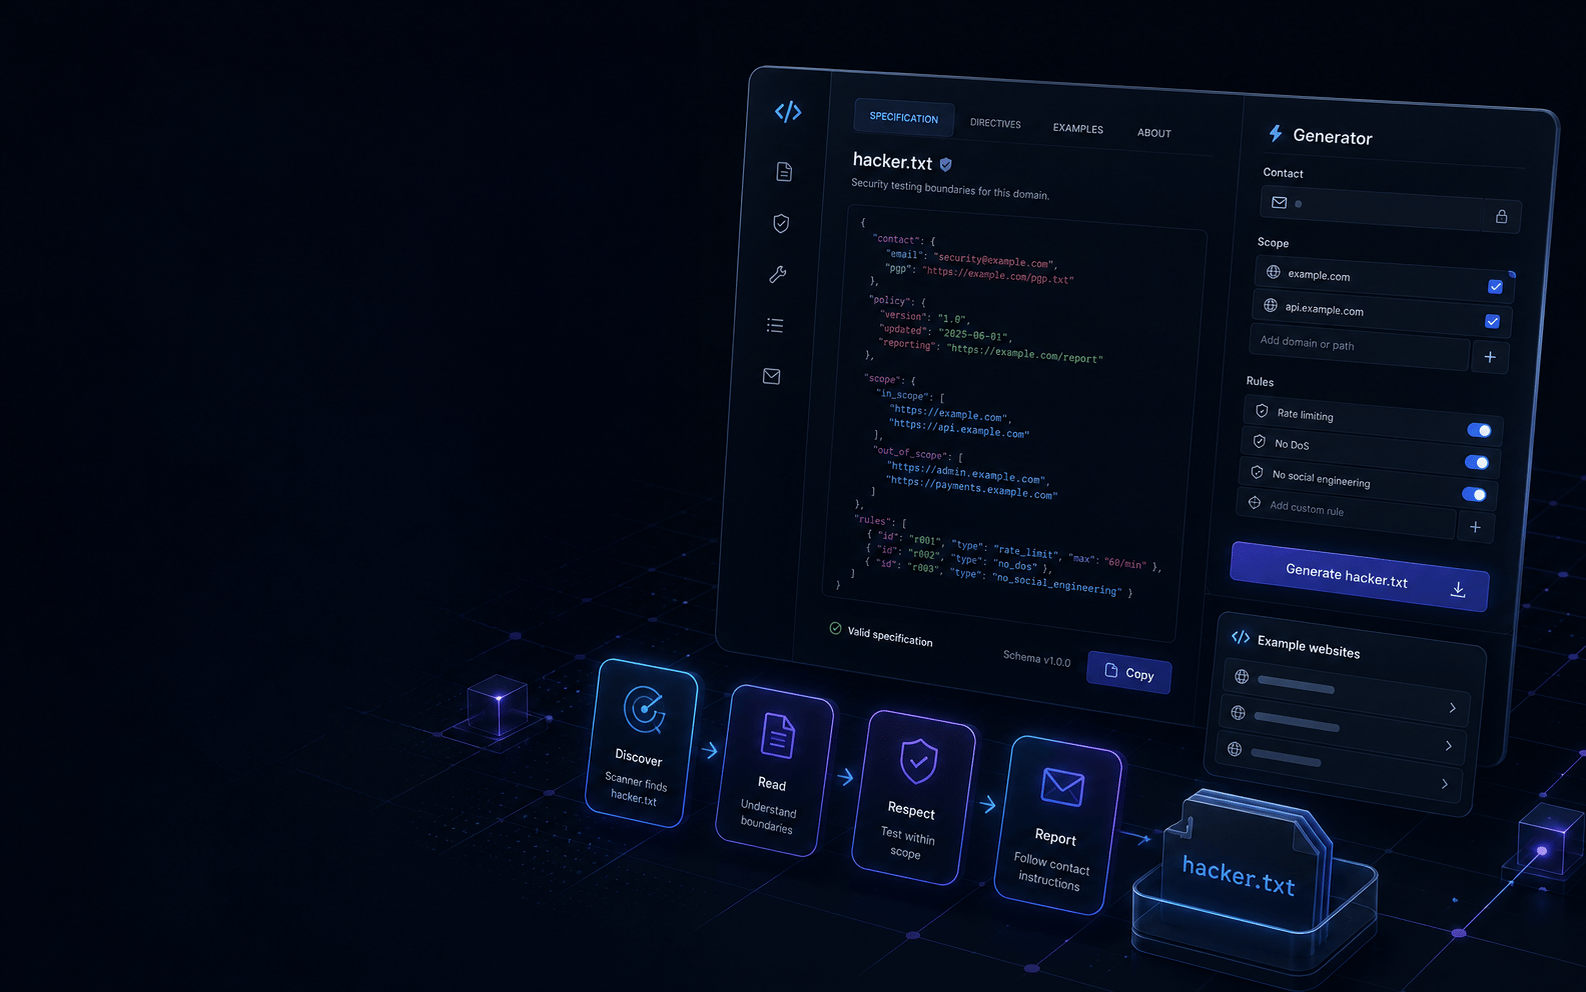
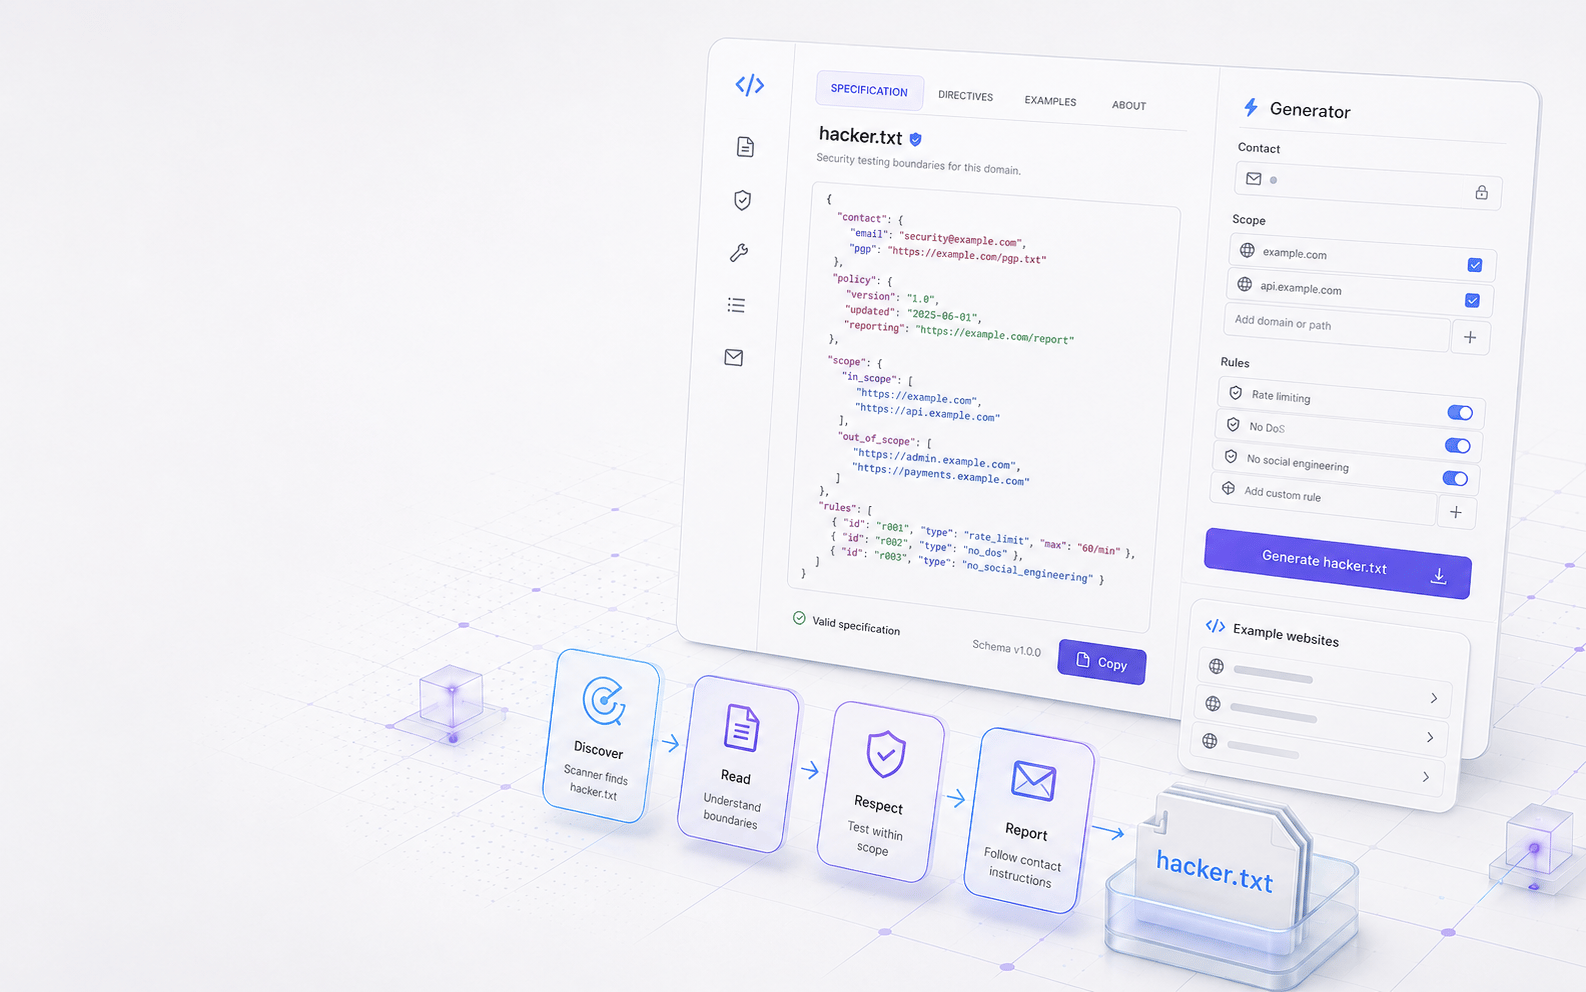
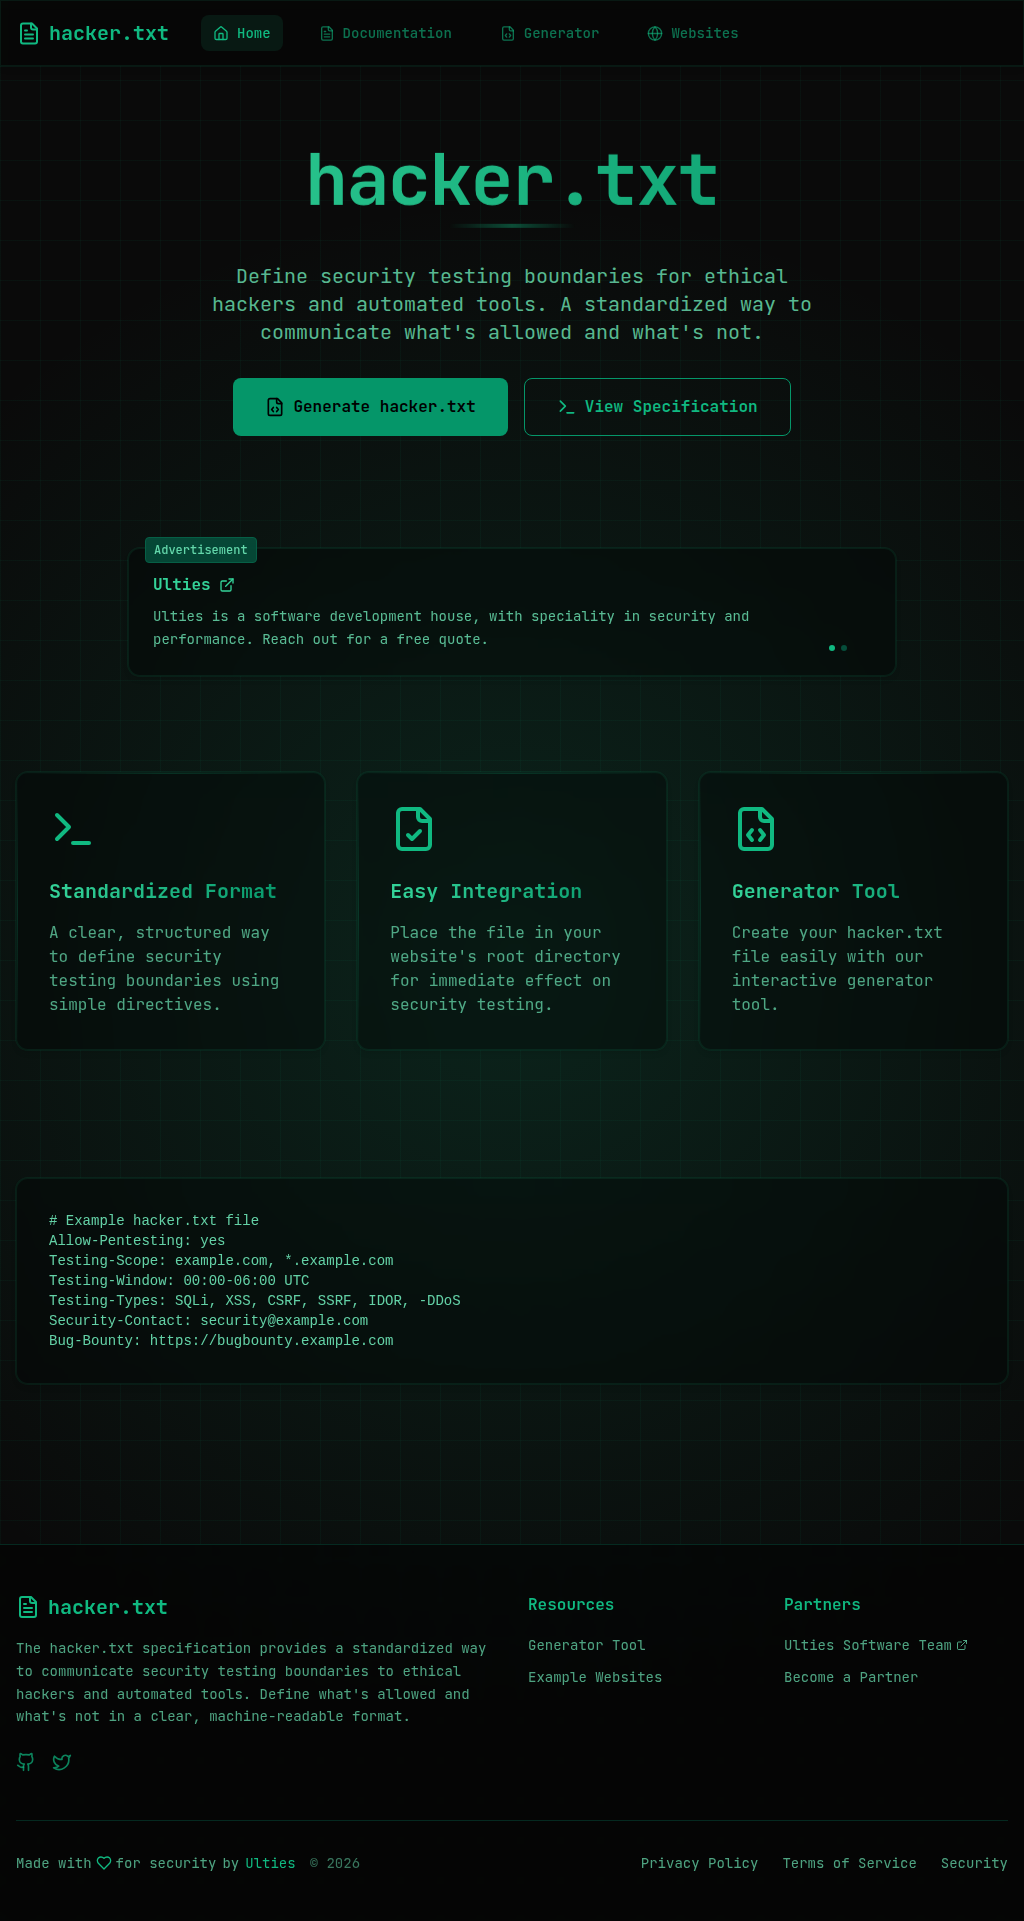
The hacker.txt site with the spec, an example directive file and the generator, on a dark interface.
Where they were stuck.
Security researchers and scanners often have to guess testing boundaries from legal pages, bug bounty programs or nothing at all. With hacker.txt, a site lists its pentesting rules, scope, contact details and disallowed activity in one standard text file.
How we shipped it.
- 01
Wrote the site around one concrete step. Put a plain-text file at the root of your domain and state your testing rules in it.
- 02
Added an example hacker.txt file, the core directives, documentation and a generator, so people can try the standard quickly.
- 03
Used the terminal-green look of security tools and kept the text clear for developers, researchers and security teams.
- 04
Wrote the docs so the file works for people and tools. It is plain text, simple to host, and structured enough for scanners to parse safely.