Laravel vs Symfony in 2026: compare maintenance and failure handling

A worked Laravel 13 versus Symfony 7.4 decision: support deadlines narrow the shortlist, while an interrupted export exposes the queue design still needed.
A support requirement can decide the shortlist
Suppose a procurement team is commissioning an internal export portal in October 2026. Its maintainers know both Laravel and Symfony. It needs upstream framework security fixes through October 2029, but cannot fund a framework major-version migration during that period. Routine patches, compatible minor releases, runtime upgrades and dependency maintenance remain funded. These are fictional constraints for a worked decision, not an Ulties customer story.
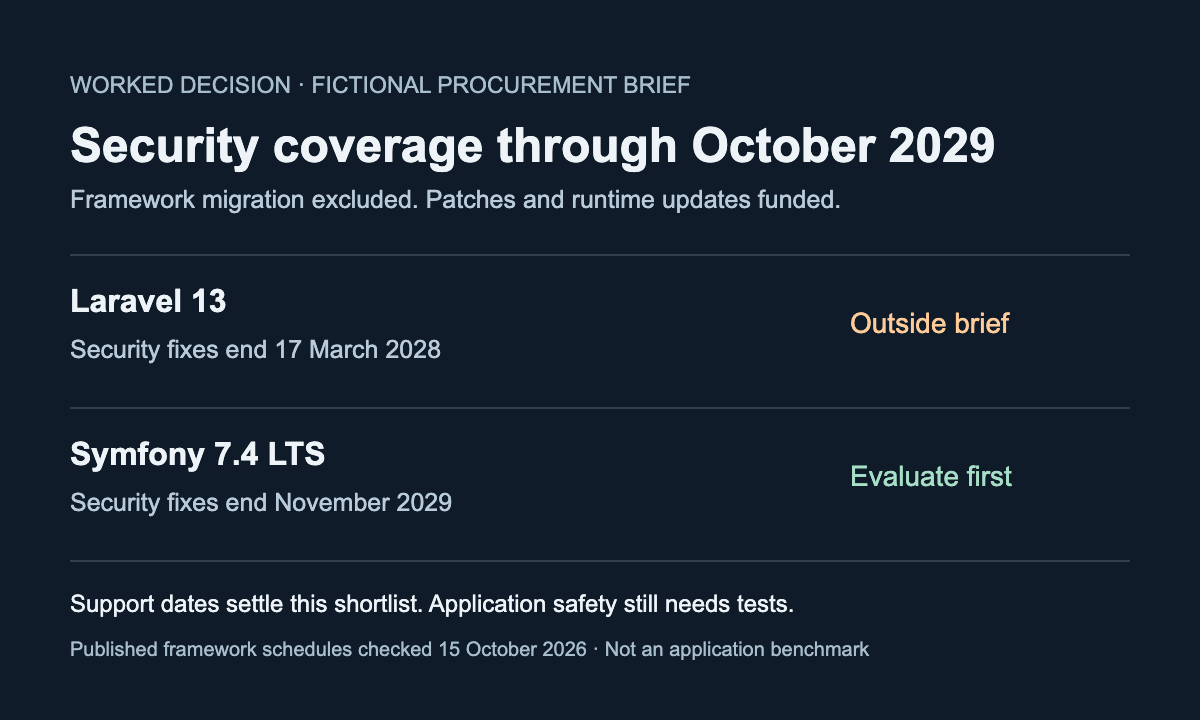
I recommend evaluating Symfony 7.4 LTS first. Laravel 13 does not cover the required period on its published security schedule. This chooses a release line to investigate. It does not approve an application design or establish which framework is faster to build with.
Compare the maintenance dates before comparing APIs
As checked on 15 October 2026, Laravel lists security fixes for version 13 through 17 March 2028 and a minimum of PHP 8.3. Symfony lists security fixes for 7.4 through November 2029, bug fixes through November 2028, and a minimum of PHP 8.2. Symfony therefore covers the fictional October 2029 security requirement. Laravel 13 does not. Security support does not promise continued ordinary bug fixes throughout that period.
A framework minimum is not a sensible instruction to freeze the runtime. PHP lists security support for 8.2 through December 2026, 8.3 through December 2027, and 8.4 through December 2028. None covers the whole example period. PHP 8.5 is listed through December 2029, but the application still needs a compatible extension and package set. My proposal is to choose a supported runtime after resolving that set, then review runtime and dependency support alongside framework support.
If procurement also requires ordinary framework bug fixes through October 2029, the Symfony option fails this brief too. The next action would be to change the maintenance requirement or fund a migration, rather than quietly reinterpret security fixes as full maintenance.
Choose the queue components explicitly
For this evaluation I would pair Symfony 7.4 with Doctrine ORM, PostgreSQL and Messenger using the Doctrine transport, plus a supervised worker and a configured failure transport. The rejected alternative would pair Laravel 13 with Eloquent, PostgreSQL, its database queue and a supervised worker. These are proposed component families, not resolved dependency locks or executed installations.
Messenger separates a message from its handler and routes asynchronous work to a configured transport. Its Doctrine transport stores messages in a database table. A failure transport must be configured if exhausted messages are to be retained there. Without one, Messenger discards messages after retries. Laravel offers queued jobs, retry controls and failed-job handling. Neither choice makes an export safe merely because it has a queue.
Follow one failed export through the proposed design
Imagine export E17 for account Cedar. The request is accepted, its record is committed, and the process dies before separately publishing its queue message. Dispatch after commit prevents a worker from reading rolled-back data, but leaves this commit-to-publication gap with an external broker. Laravel documents after-commit dispatch and discarding jobs on rollback; that is not a claim of an atomic database-and-broker transaction.
For this example, I prefer writing the export request and an outbox entry in the same database transaction and letting a publisher retry delivery. This adds a publisher, backlog monitoring and recovery work. Using a database-backed transport might offer another design, but it requires checking the actual connection and transaction participation. A shared database name, a Messenger transaction middleware setting or a database queue driver alone is insufficient evidence of the producer boundary.
Now let the worker produce E17’s private file and die before recording completion. Redelivery must not publish a second conflicting result. My design judgment is to bind E17 to a fixed data snapshot, use attempt-specific temporary objects, and conditionally record the winning object against the export row. A later attempt should reuse a recorded completion, while stale attempts cannot replace it. File storage and the database do not become one transaction: abandoned objects still need cleanup. This design needs concurrency and interrupted-upload tests before release. None was run for this comparison.
Recovery settings belong in the decision
Both alternatives need a policy for an export that never finishes. Laravel warns that the worker timeout must be shorter than the queue retry interval to avoid overlapping processing. Symfony’s Doctrine transport warns against a redelivery timeout shorter than message duration and supports keepalive updates. These controls reduce accidental overlap. They do not replace the conditional completion rule.
For the Symfony trial, I would require an operator to locate E17 in application state and the failure transport, identify the cause, and decide whether replay remains valid for its data snapshot. A permanently invalid export should show a useful failure instead of entering endless manual retries. Deployment also needs worker replacement and message compatibility checks. Those are proposed release gates, not observations from a running portal.
What would change the recommendation?
I would reopen the Laravel option if the buyer funds major-version upgrades before its security deadline, or if a required integration cannot be maintained on Symfony 7.4. If the actual team only knows Laravel, the training and ownership cost also needs a real estimate. No hiring, delivery-time or performance evidence was collected here.
The useful result is a conditional choice: Symfony 7.4 reaches the stated framework security horizon, with a separately funded runtime and dependency plan. It still needs a locked installation and tests of authorization, transaction boundaries, redelivery, concurrency and operator recovery. Support dates settle the shortlist in this example. They do not certify the software.