

Default-deny egress control for agent containers
Outcall is an open-source host firewall daemon, with operator controls, for outbound traffic from Docker agent containers. It denies everything by default, using nftables, DNS filtering and an HTTP proxy.
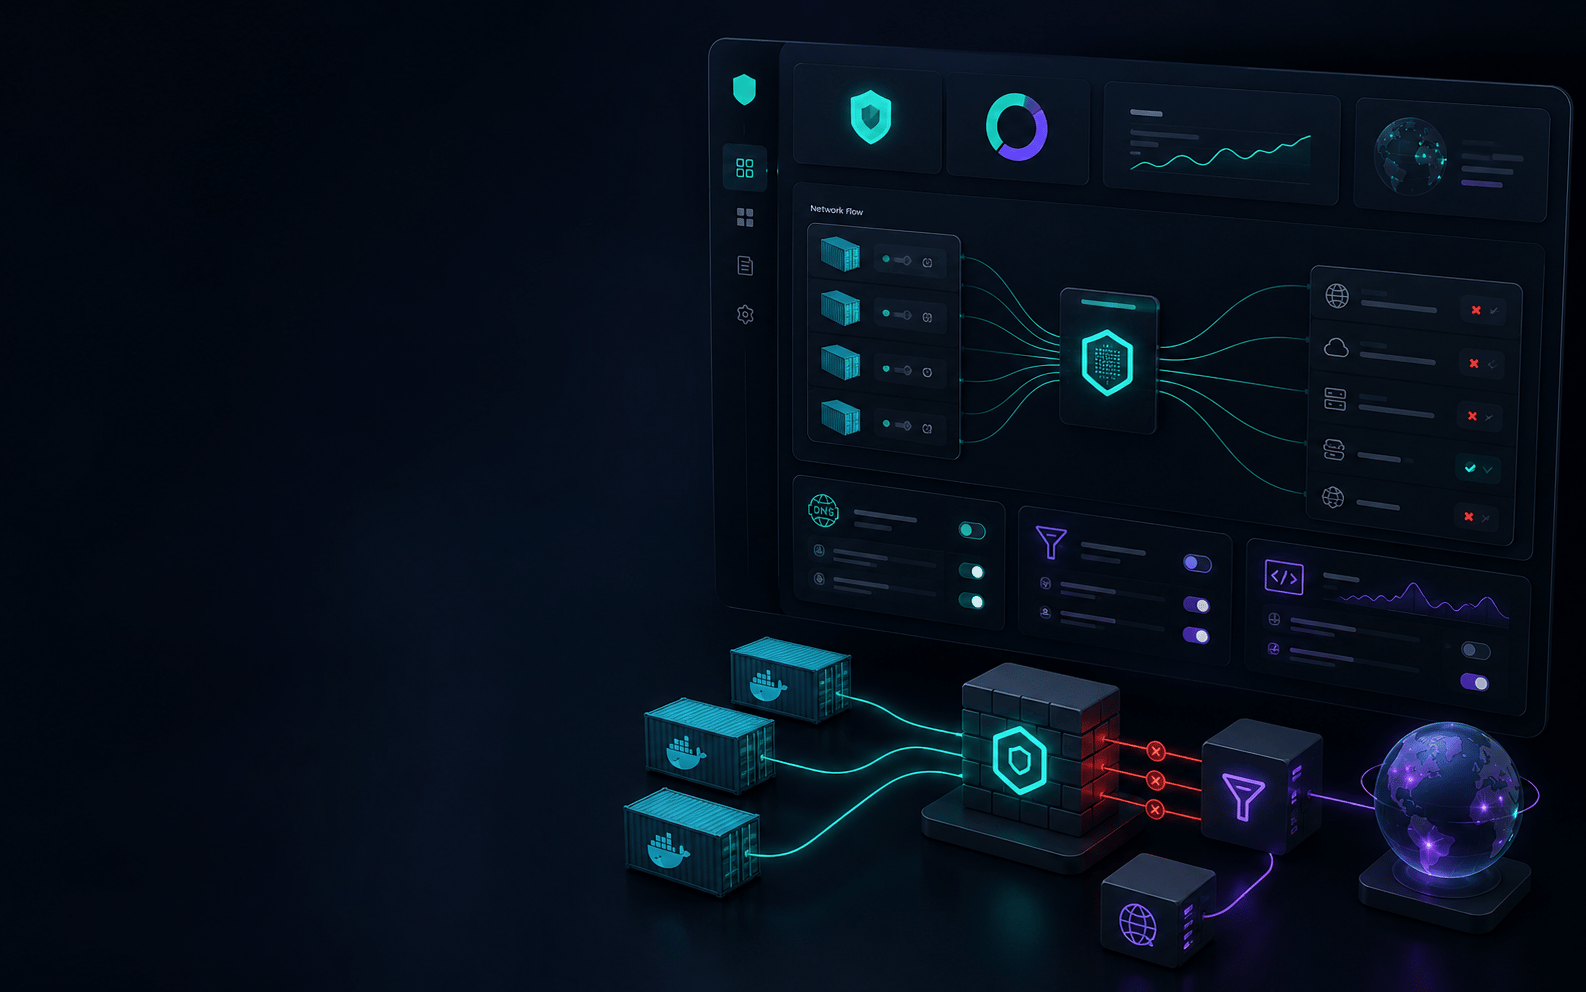
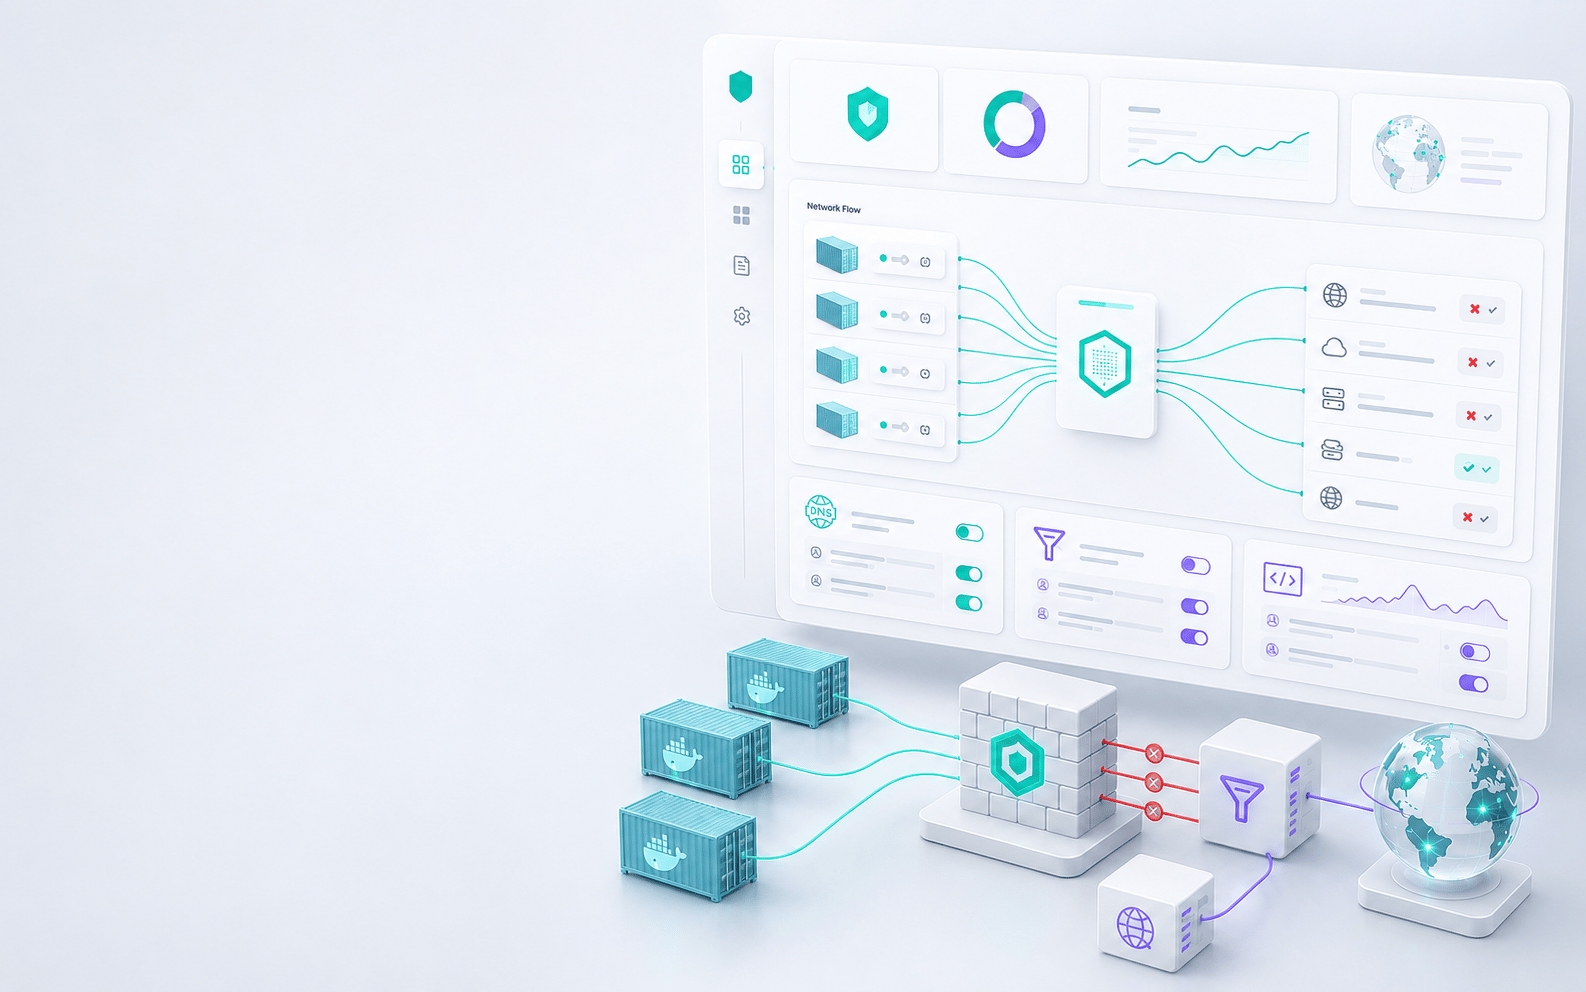
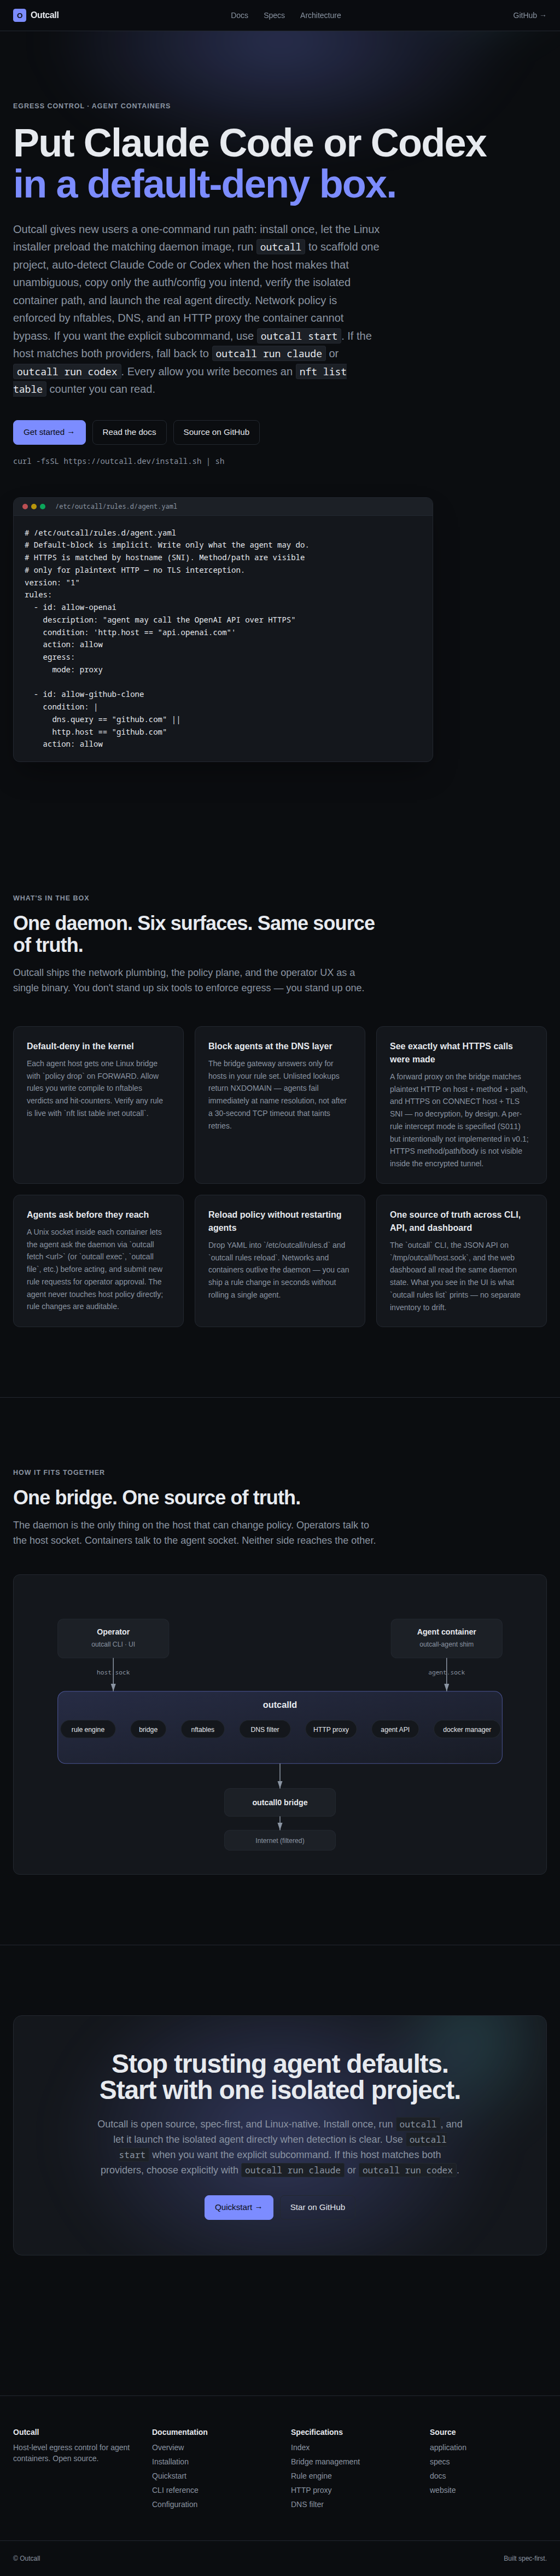
The site opens with the operator problem. Put Claude Code or Codex in a default-deny box, then make each outbound permission explicit and enforced.
Where they were stuck.
Teams running coding agents needed more than loose network isolation. They wanted to isolate containers, block outbound traffic by default and allow narrow access by hostname, method, path and agent identity, without trusting the agent to behave.
How we shipped it.
- 01
Explained the setup. One command starts it, a daemon runs on the host, a bridge owns outbound policy, and six interfaces share one source of truth.
- 02
Wrote plain explanations of how nftables, DNS filtering and the HTTP proxy work together to enforce the rules.
- 03
Wrote the site for operators who want Claude Code or Codex in a default-deny box, with outbound access they can audit.
- 04
Shipped the docs and product site, so users can understand the security model before they open the repo, the specs or the daemon code.